Firing the top cyber official after a week of broken flights, frozen bank transfers, and glitching agency networks feels decisive. Honestly, it's mostly political theater.
When the White House moved to oust National Cyber Director Sean Cairncross amid a string of high-profile technology outages in November 2026, the move looked like an immediate answer to public frustration. Planes were grounded, Microsoft workplace tools stumbled, banking transactions hit snags, and even an internal National Security Agency network ran into trouble during scheduled maintenance. Swapping out the person in charge is fast and visible. Fixing brittle software pipelines and aging infrastructure takes years of unglamorous engineering work.
What people really want to know when everything breaks at once is simple: Were we hacked, or did our own systems just fall over? According to senior U.S. officials—including Director of National Intelligence Jay Clayton—intelligence reviews and company statements pointed to internal faults, updates, or maintenance rather than a coordinated nation-state cyberattack. Still, removing Cairncross—who had been in the role since August 2025 after earlier political and White House work—and naming Pentagon Chief Information Officer Kirsten Davies as acting replacement puts a spotlight on who holds real technical authority in Washington.
What Happened During the Outage Wave
A single glitch is a headache. Four or five major disruptions stacking up across consecutive business days makes everyone jumpy.
Between Thursday, November 12, and Tuesday, November 17, 2026, Americans watched critical systems hiccup one after another. Microsoft 365 ran into trouble starting around 11:20 a.m. ET on November 12, hitting Outlook email and dependent Teams features before recovery dragged into the next day. On Friday, November 13, the Federal Aviation Administration halted U.S. departures for more than four hours—a nightmare right ahead of busy fall travel—with preliminary reporting pointing to a contractor line-migration issue rather than a malicious intrusion.
Then came Monday and Tuesday. Chase customers reported delays with transactions and Zelle payments on November 16. By Tuesday, November 17, Apple services like Apple Music, the App Store, and AppleCare faced disruptions tied to an internal update, Marriott reported sign-in snags, and the NSA acknowledged temporary degradation on an internal classified communications network during scheduled routine maintenance.
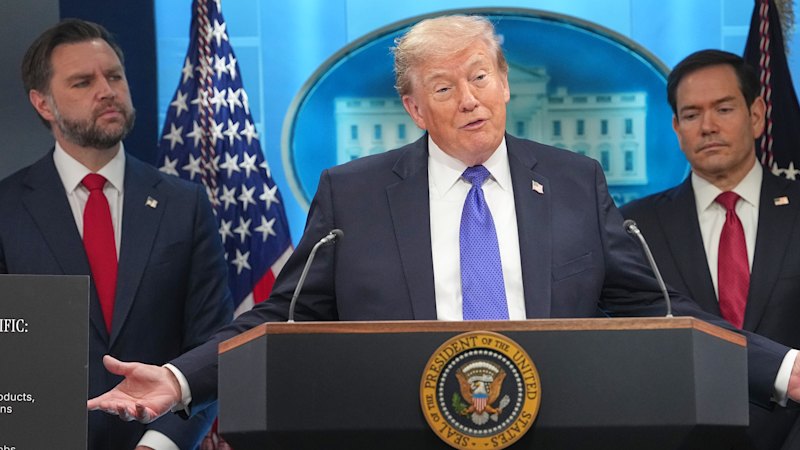
President Donald Trump downplayed the run of glitches as inevitable—"Things like that happen"—while congressional leaders pressed the administration for briefings and transparency. Even with officials ruling out a coordinated foreign attack, skeptics and security analysts raised a fair point: ruling out an intrusion fast can look reassuring, yet thorough forensics take time.
Why Removing a Cyber Chief Misses the Real Bottleneck
If you've ever run production systems under heavy load, you already know why firing a policy coordinator doesn't magically make software stable.
The Office of the National Cyber Director was created in 2021 to coordinate federal cyber policy and strategy, not to push patches to airline routers or rewrite cloud gateway code. Reports around Cairncross's removal focused heavily on credentials—sources cited concerns from senior White House figures that he lacked deep technical cyber credentials for the job. Having technical chops at the policy table matters, especially as AI security frameworks and threat sharing sit high on the agenda. Bringing in Kirsten Davies in an acting capacity adds experienced defense IT leadership.
Still, a title change doesn't fix three structural problems sitting right in front of us:
- Monocultures amplify every mistake. When huge swaths of business email, financial rails, aviation telecom, or consumer platforms rely on narrow sets of vendors and shared network paths, one bad update or latent bug ripples outward fast.
- "Not a hack" isn't the same as "safe." Outages caused by configuration errors, faulty updates, or maintenance slips hurt operations just as badly as an attacker's payload—and can even create blind spots while teams scramble to restore service.
- Leadership vacancies slow momentum. While Washington debates cyber leadership and wrestles with other Senate confirmation battles—including scrutiny around the nominee to lead the Cybersecurity and Infrastructure Security Agency—day-to-day resilience often gets stuck in neutral.
That's the part I wish more coverage emphasized. We tend to treat cyber defense and operational reliability as two separate buckets. In practice, fragile, poorly tested systems are a gift to both accidental downtime and real adversaries.
Credibility, Transparency, and What Experts Are Debating
There's real debate here, and pretending otherwise would be dishonest. On one side, administration officials and affected companies maintain there's no evidence of a coordinated cyberattack and argue these events stem from separate technical and maintenance issues. On the other side, lawmakers and outside analysts—including former defense analyst Mike Wiacek—have questioned how quickly officials dismissed malicious activity and urged deeper scrutiny before drawing neat conclusions.
Both concerns can be true at once. A latent bug in a networking component or a botched line cut during maintenance can knock systems offline without any foreign espionage involved. At the same time, public trust takes a hit when high-profile outages stack up and officials sound dismissive or rush to close the book.
Practical Steps You Can Take Right Now
You don't control federal appointments or cloud vendor release cycles, kinda frustrating as that is. You can stop assuming your tools will stay up every hour of the day.
- Build a low-tech fallback for critical tasks. Keep offline copies of essential confirmation numbers, emergency contacts, and basic operating procedures so a locked-out email inbox or stalled app doesn't bring your day to a halt.
- Don't rely on a single payment or communication rail. If you run a business or manage household bills, have a secondary payment method and an out-of-band way to reach teammates or clients when primary platforms glitch.
- Test your own recovery plan before an outage hits. Schedule a quick tabletop check with your team or family: if your primary cloud account, transit route, or banking app goes down for four hours, who does what first?
- Watch post-incident reports, not just day-one headlines. Initial explanations during an outage are often preliminary. Check follow-up technical disclosures from vendors and agencies to see whether the root cause was a rushed update, a single point of failure, or a security gap that needs closing.